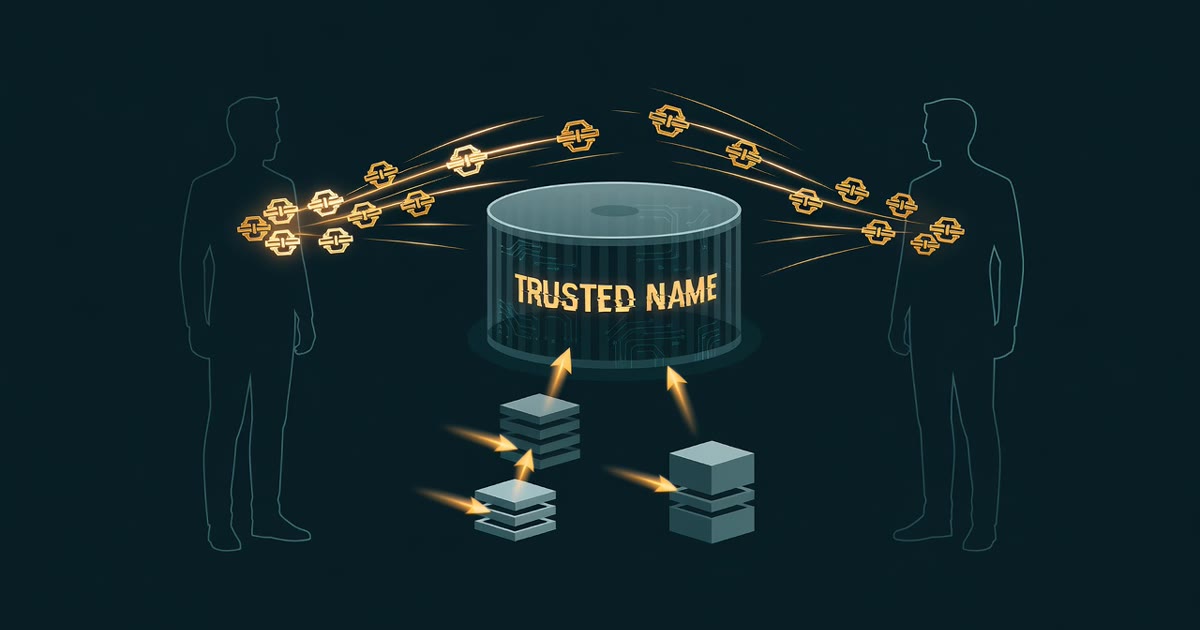
Docker disclosed CVE-2026-105445 on 12 October 2026. From 26 August 2024 until a fix on 30 September 2026, converting a personal Docker Hub account into an organization reassigned that account's personal access tokens to the named new owner without rotating or revoking the secret. The new owner was not asked and was not told.
What happened
The attack is simple and authenticated. Create an account, mint a PAT, convert the account to an organization, and name a target user as owner. The attacker's token then authenticates to the registry as the target, within the token's scopes. That includes pull, push, and delete on repositories the target can reach, including organization repositories. Publishing an image under a name other people already trust is why Docker rated it critical: CVSS 4.0 9.4.
It did not open the Docker Hub web UI. It could not change the target's password, email, or two-factor settings, and it was not a full account takeover. Researchers Peter Molnar and Krisztian Hozak reported it on 30 September. Docker says it reproduced the issue and deployed a fix the same afternoon, about four hours after the report. Conversion no longer transfers PATs.
Docker reviewed every conversion in the window and about 304,000 pushes made with transferred tokens. It says none of those pushes landed in an unrelated account, and a static review of the highest-risk public images found no malware. Docker is explicit about the limit of that finding: a transferred token that was never used leaves no registry trace. On 8 October it deactivated transferred PATs except where the owner asked to keep them.
Who is affected
- Docker Hub accounts that received a PAT through account-to-organization conversion between 26 August 2024 and 30 September 2026
- Organizations those users administer, because a pushed image can ride a trusted name
- Anyone who pulls images from a namespace that went through that conversion
Docker emailed exposed users and organization owners on 2 October with the subject "Docker Hub Vulnerability Identified & Resolved". If that mail never arrived, Docker says no PAT on the account moved through this flow.
What to do now
Search mail for Docker's 2 October notice, and if you got it, treat every listed token as burned even though Docker later deactivated them. In Docker Hub, open Account settings, Personal access tokens, and revoke anything you do not recognize. Move organization automation off personal PATs and onto organization access tokens.
If a namespace you pull from was in the exposed set, pin digests for production pulls and review images pushed between 26 August 2024 and 8 October 2026. Docker's own review found no malicious pushes. That is not a substitute for checking the namespaces you actually depend on.
Source: Docker, Docker Hub security advisory: CVE-2026-105445.
Also on the blog
- CVE-2026-104935: Ivanti Connect Secure auth bypass exploited since Oct 3
- CVE-2026-96951: Windows Shell MOTW bypass exploited, patch by 16 Oct
- GitLab CVE-2026-97229: CVSS 10.0 unauthenticated RCE
- CVE-2026-39919: Ghostscript CVSS 9.8 PDF heap overflow
Next step: If this is on your network or a client's, ask Matthews Enterprises to check exposure.